
The Agentic AI Autopilot for Identity Security
90% of breaches start with a compromised identity. While most tools just generate alerts, Sharelock investigates and responds.
The only European ITDR platform recognized by Gartner and GigaOm. Built under EU law. Designed to stop identity attacks before your analyst reads the first alert.
Recognized by:
Sharelock recognized in the latest Gartner report for our pioneering Agentic AI technology.
READ MORE
GigaOm names Sharelock a Leader and Outperformer in the 2026 GigaOm Radar for ITDR.
READ MORE
THE PROBLEM: THE IDENTITY THREAT LANDSCAPE
No one breaks in. They just sign in with your credentials.
Password attacks happen 7,000 times per second, and credentials are for sale on the dark web before your security team finishes their morning coffee. When an attacker signs in with a legitimate identity, most tools don't notice — because nothing looks wrong.
The real bottleneck isn't detection. It's what happens after the alert fires — while a human analyst investigates manually, the attacker is already escalating privileges and moving laterally.

First Attack Vector
80
%
Cloud Intrusions
75
%
of increase y-o-y of intrusions into the victim's cloud using valid credentials.
Exposed Attack Surface
25
%
of all attacks start from unprotected identities such as contractors', inactive or over-provisioned accounts.
THE SOLUTION: THE SHARELOCK PLATFORM
See the attack. See the call. See it closed. Autonomously
From the first suspicious login to a closed, audited case, Sharelock's Agentic AI handles the entire investigation, so your analysts don't have to.

How Do You Catch an Attack That Looks Like Normal Behavior?
Watch how Sharelock's Agentic AI tells the difference — and shuts down the threat before anyone has to ask.
THE SOLUTION: THE SHARELOCK PLATFORM
One platform, limitless security
Unify human and non-human identities across on-prem and cloud environments, replacing point solutions with a single, comprehensive identity security platform.
Prevent
Identity Security Posture Management
Discover and close identity gaps before attackers find them. Automated hygiene for misconfigured accounts, orphaned privileges, shadow admins, and non-compliant access across hybrid, cloud, and on-prem environments.
Explore PreventionDetect
Identity Threat Detection
No static rules. No alert storms. Sharelock's behavioral AI monitors every access event and entity behavior to detect credential misuse, privilege escalation, and lateral movement in real time, across every environment.
Respond
SIA - Security Investigation Autopilot
The case is closed before your analyst reads the alert. SIA autonomously correlates signals, maps the attacker's path, enforces remediation, and generates a complete audit trail without a single manual query.
AI-Driven Identity Security: Precision, Speed, Efficiency
Revolutionize identity protection with advanced AI that accelerates investigations, automates responses, and enforces security posture.

Investigate and Respond Instantly

Enforce Proactive Identity Security

Boost Efficiency with Automation
AGENTIC AI vs AI ASSISTANT
Your SOC doesn't need another copilot. It needs an autopilot.
Every vendor says 'AI.' Most just answer your questions.
SIA doesn't wait to be asked, SIA investigates, maps the attack, and remediates on its own
THE LEGACY WAY
AI Copilot (Other Vendor)

You ask → it answers

90% of the analyst workload stays manual

Overnight Operation waits for input

Audit trail summary on request
THE AUTOPILOT WAY

Alert → it investigates on its own
−80% investigation time
Works 24/7, autonomously
Complete, explainable, compliance-ready audit trail
Every vendor says 'AI.' Most just answer your questions. SIA doesn't wait to be asked — it investigates, maps the attack, and remediates on its own
THE ONLY EUROPEAN ITDR LEADER
The only european ITDR Leader.
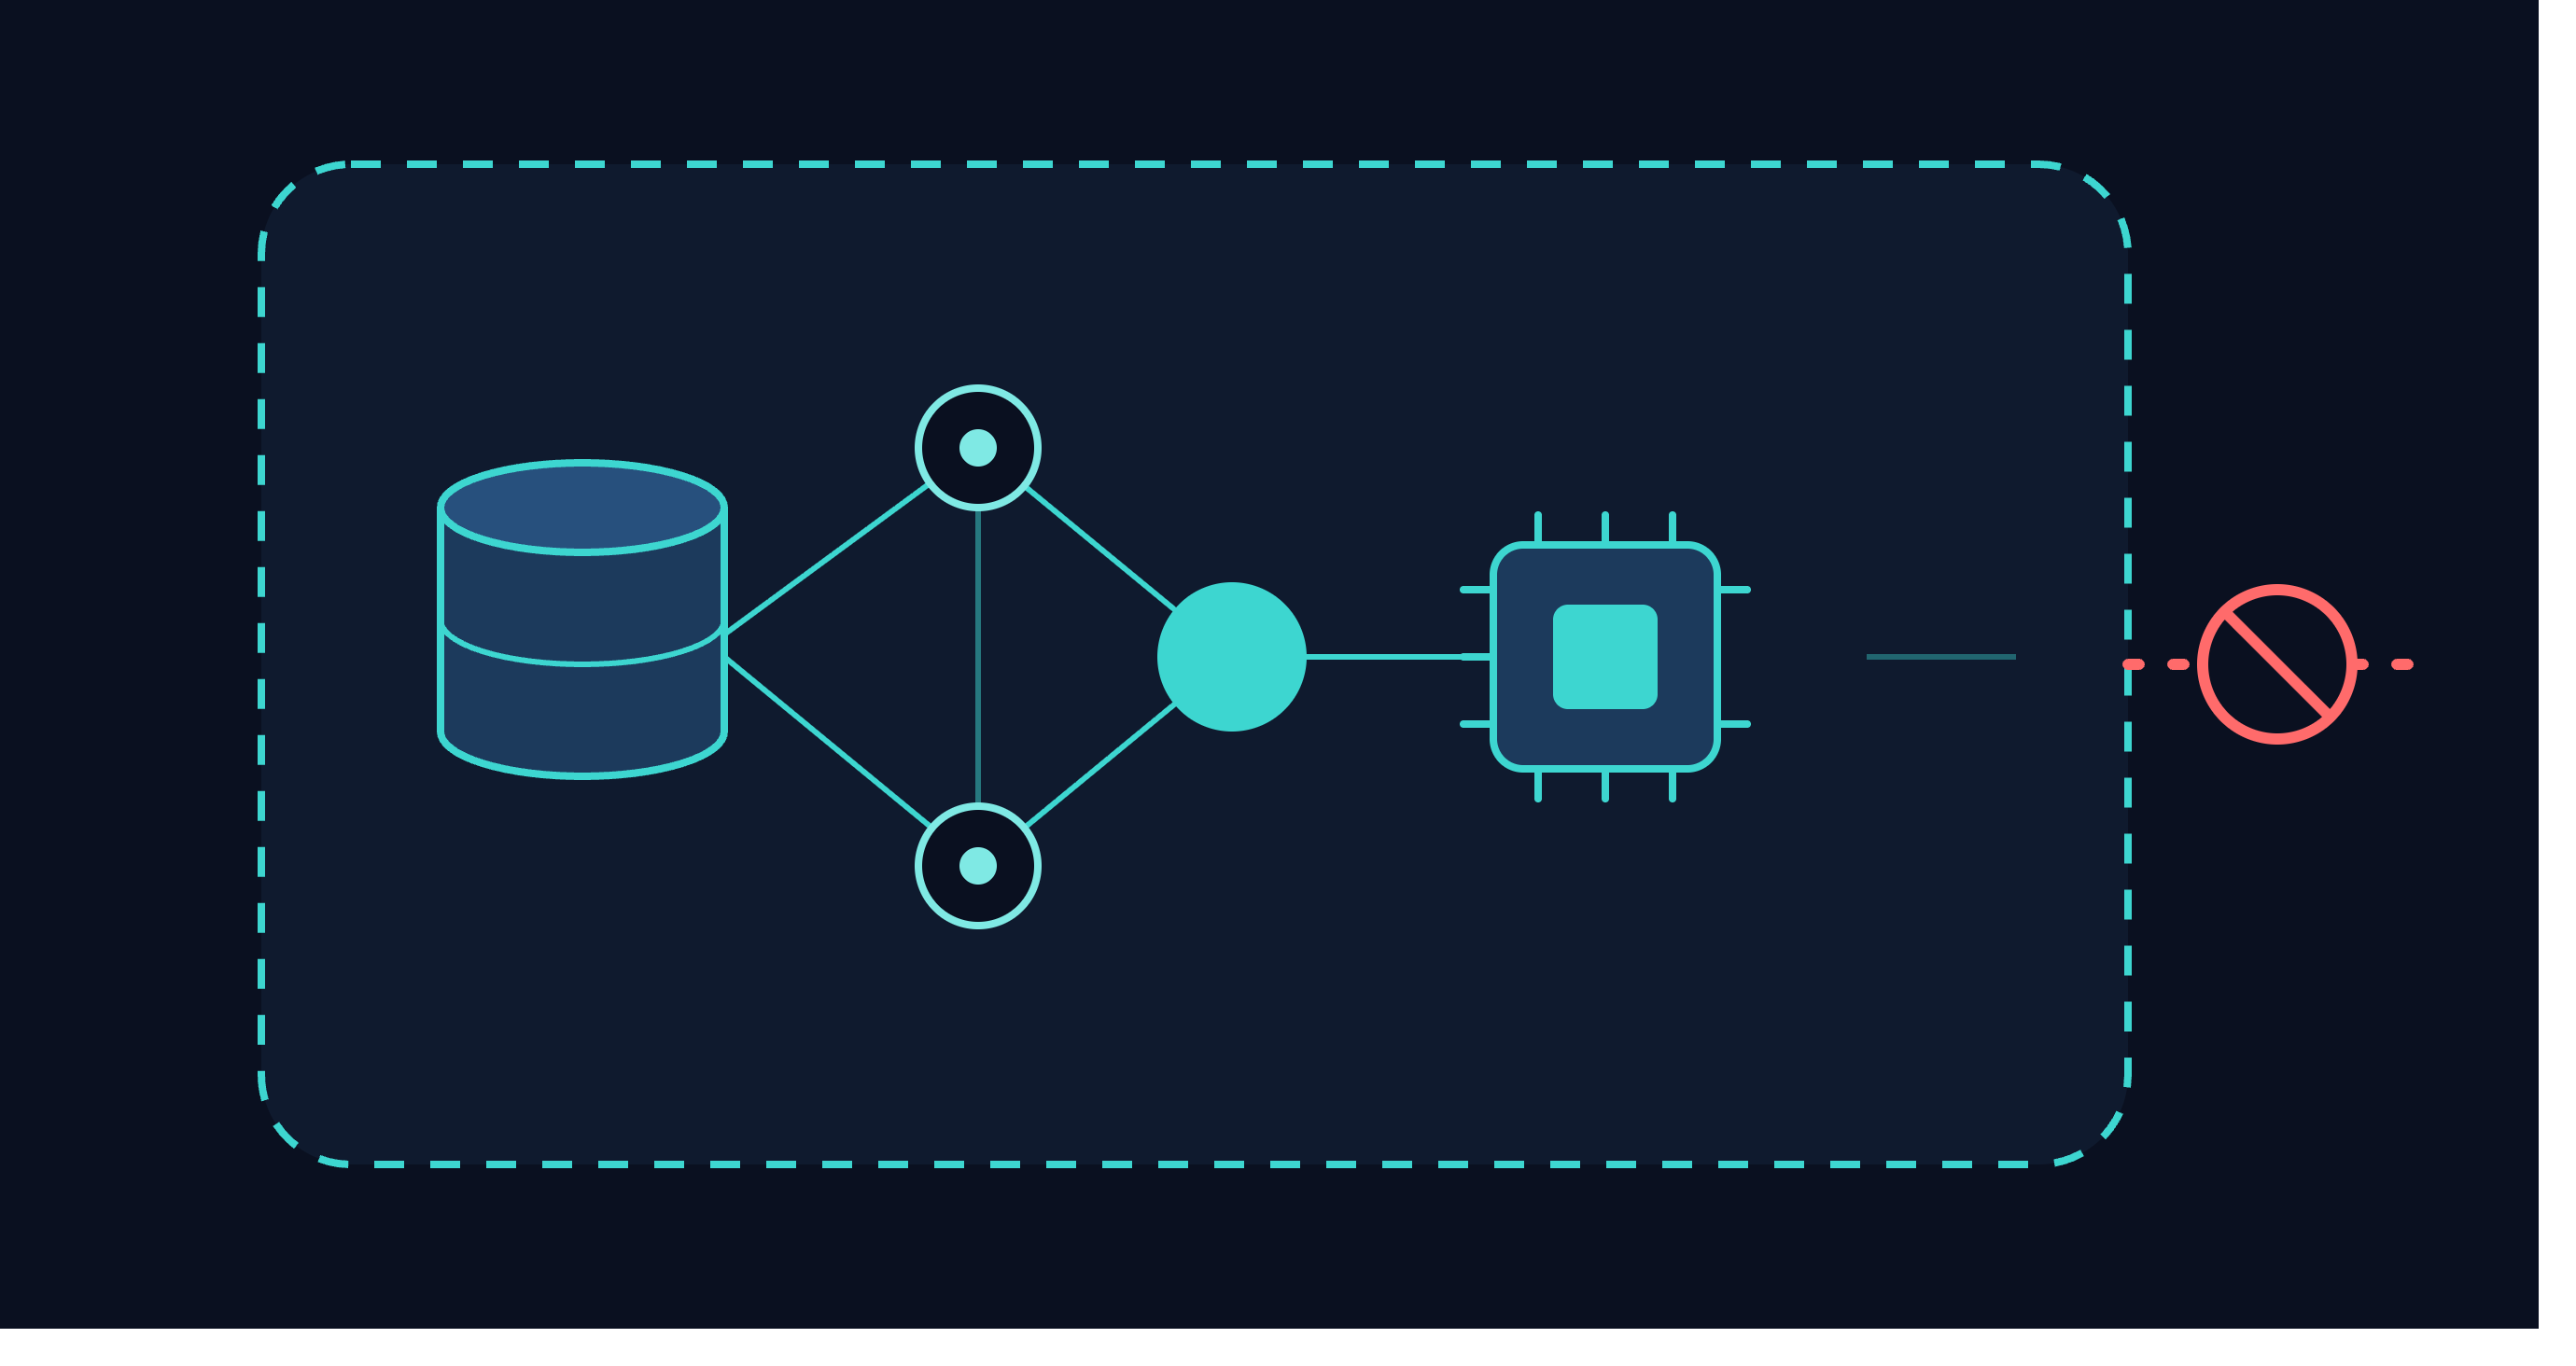
Built under EU law, not adapted to it
NIS2 Compliant
DORA Ready
GDPR Native
Sovereign Cloud
Most other vendors in the GigaOm ITDR Radar are US-based, putting your data under the US CLOUD Act. None are European. Sharelock is built in Rome under GDPR, aligned with NIS2, DORA, and the EU AI Act, qualified and listed in the official catalog of the Italian National Cybersecurity Agency. Not a differentiator, it's a requirement.

Data processing designed under EU law, not retrofitted after US-first architecture.
Built to meet EU regulatory requirements without additional compliance tooling or custom configurations.
Your identity data, investigation logs, and audit trails stay in European jurisdiction.
40%
+30% in 2023-24
of European enterprises now use sovereign cloud solutions, up from 30% in 2023–2024, with a further 31% planning to adopt it.
Validated by Analysts, trusted by Security Teams
The only European company recognized by Gartner as Agentic AI Tech Leader, in the KuppingerCole ITDR Compass 2025 as Innovation Leader and in the GigaOm ITDR Radar 2026 as Leader and Outperformer.
Customer experience

From compromised login to closed case — Watch the Clock
This is what happens inside Sharelock when an identity alert triggers. No tickets, no handoffs, no waiting.
How Sharelock Works
0
second

A login looks normal. It isn't.
An employee's credentials are used from a new device, at an unusual hour. Nothing trips a static rule. Sharelock's behavioral AI flags the anomaly instantly.
32
seconds

Agentic AI starts investigating. No human involved yet.
Agentic AI correlates the login with access patterns across the entire identity estate, maps what the account touched next, and reconstructs the attacker's path
Outcome

The case closes. Your team never touched it.
Access is revoked, the session is killed, and the incident is fully documented, the same automation that delivers 86% faster response and saves security teams hundreds of investigation hours.
Privileged accounts are the highest-value target in any organization. Sharelock monitors every privileged session, flags behavioral anomalies, and autonomously contains suspicious activity, before escalation.
SEE MORE
Attackers move laterally through your environment using legitimate credentials. Sharelock maps the movement path in real time and cuts the chain before they reach critical assets.
SEE MORE
Insider threats don't trigger malware alerts, they log in like everyone else. Sharelock's behavioral AI spots the deviation from normal, autonomously investigates intent, and stops escalation before damage is done.
SEE MORE
Non-human identities like service accounts, API keys and AI agents are often over-privileged and under-monitored. Sharelock discovers, assesses, and protects every non-human identity in your environment.
SEE MORE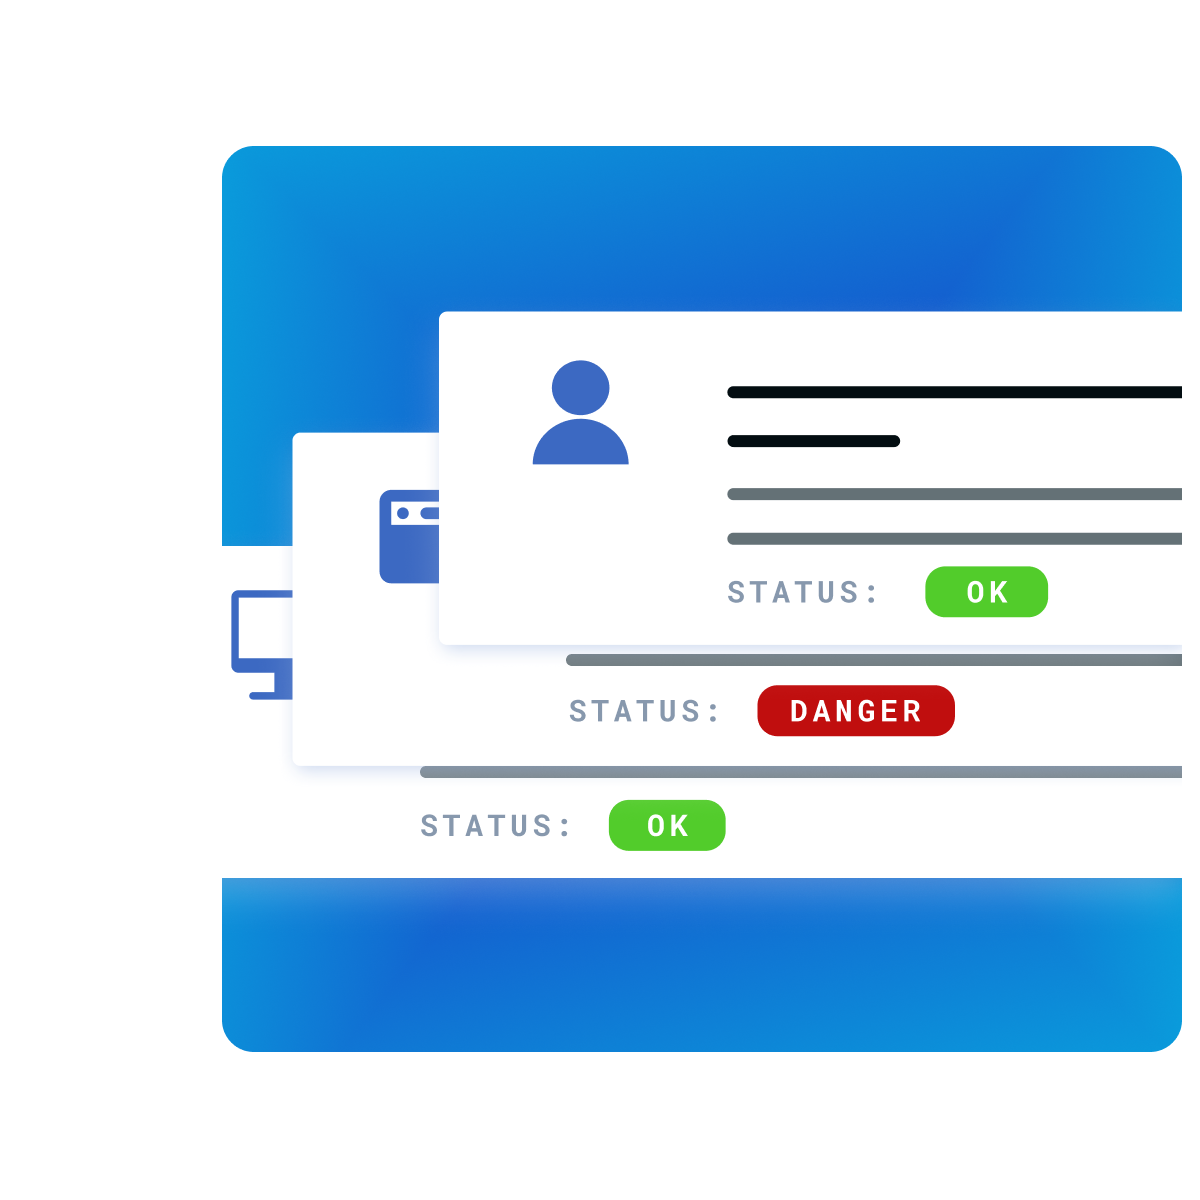
NIS2 and DORA require documented incident response, continuous monitoring, and fast breach reporting. Sharelock's audit trail and autonomous investigation satisfy both regulatory and security requirements simultaneously.
SEE MORE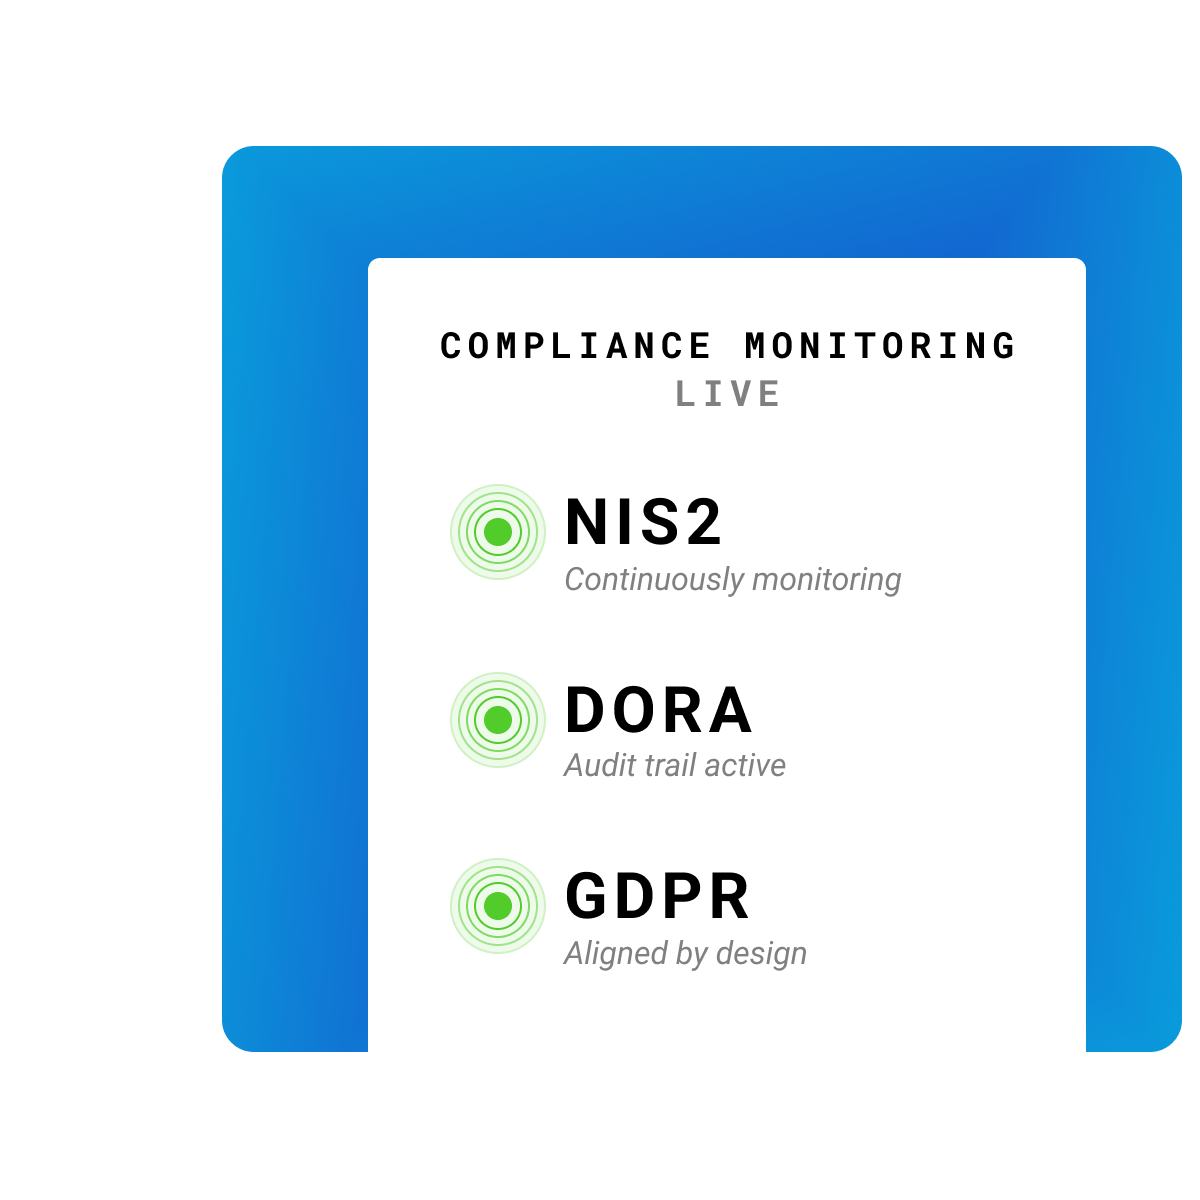
Excessive permissions and missing MFA are the silent gaps attackers count on. Sharelock continuously identifies overprovisioned accounts and authentication gaps, enforcing least privilege and MFA automatically across every identity.
SEE MORE
October 27, 2026

October 27, 2026
October 27, 2026

The leading Agentic AI Autopilot for autonomous identity threat detection and response (ITDR) and cloud entitlement protection.




