
They have the password, but they don’t have the behavior
Traditional ITDR stops at the login screen. Sharelock’s behavioral AI monitors the entire session—post-access, across multi-cloud and proprietary legacy systems. We detect lateral movement and privilege escalation in real-time, instantly blocking the identity, not the device.
Ask for a demoTHE PROBLEM
Attackers don’t hack in. They log in.
Identity is the new perimeter, but traditional security tools stop monitoring the moment authentication succeeds. Once inside, attackers exploit valid credentials to move undetected.

Valid credentials
75
%
Weak authentication
78
%
of organizations struggle with breaches caused by inadequate authentication methods
Lateral threats
292
days
to detect breaches with stolen credentials. Adversaries move laterally undetected with valid credentials
The 3 core friction points

Post-Access Blind Spot
Chronic Alert Fatigue
SOC teams waste hours manually investigating noise while real identity attacks unfold undetected.
Human-Speed Defenses
Attackers move at machine speed; human analysts relying on static rules cannot react in time.
HOW IT WORKS · THE AI ADVANTAGE
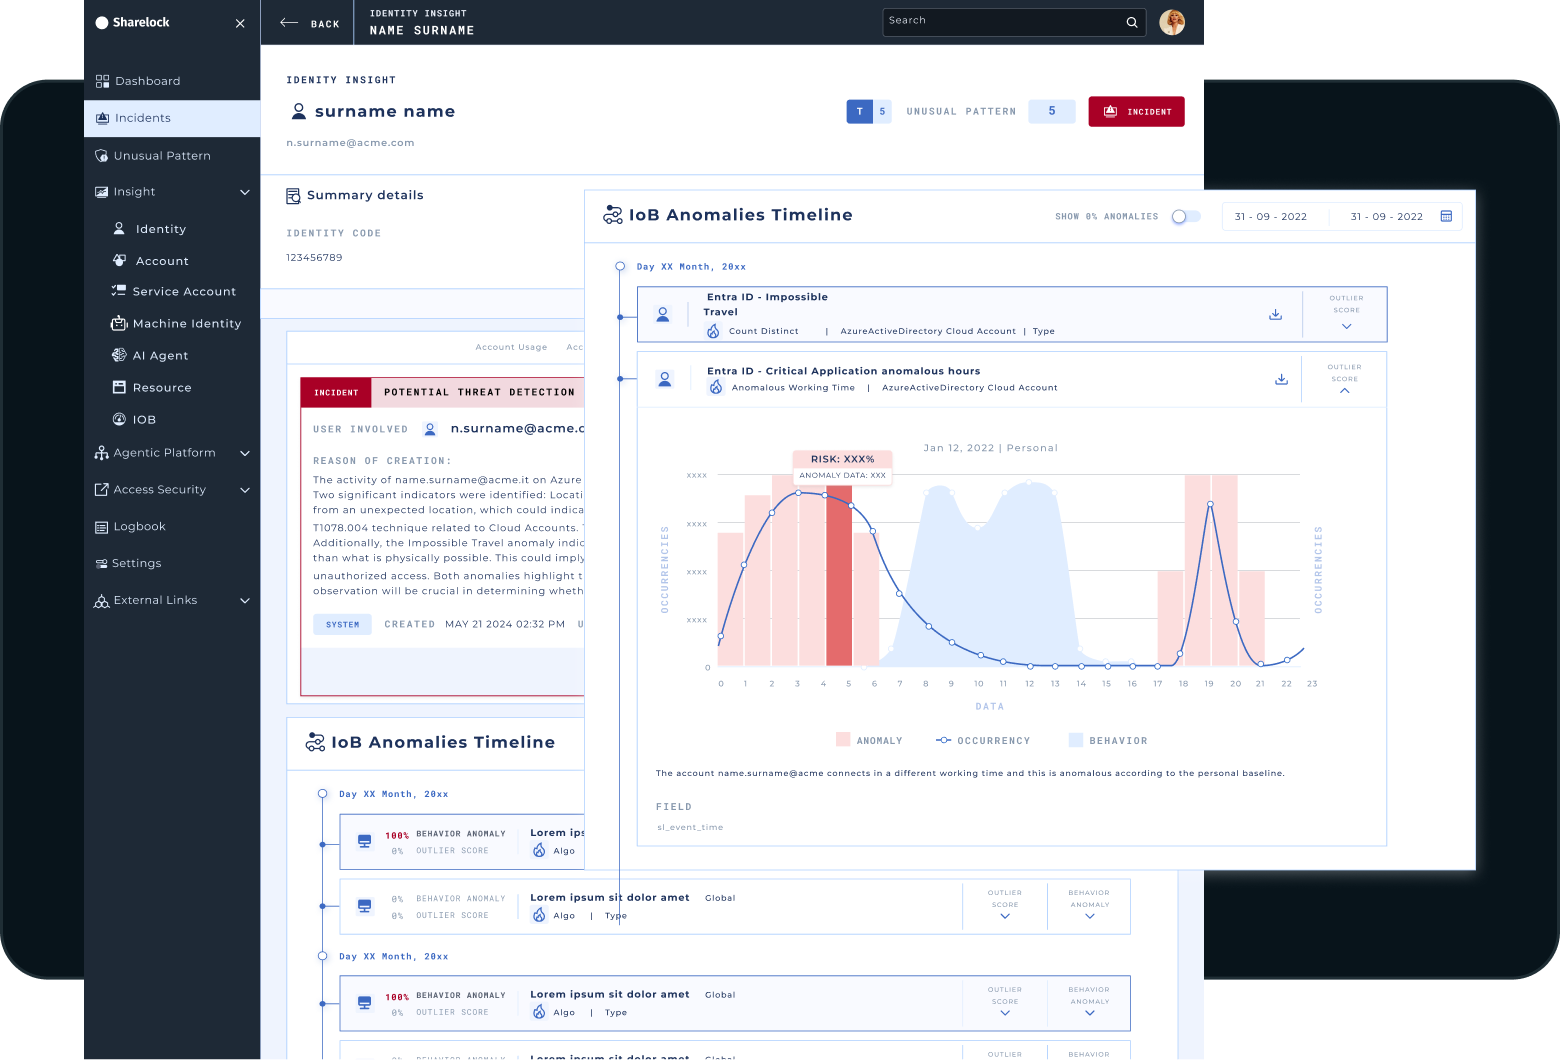
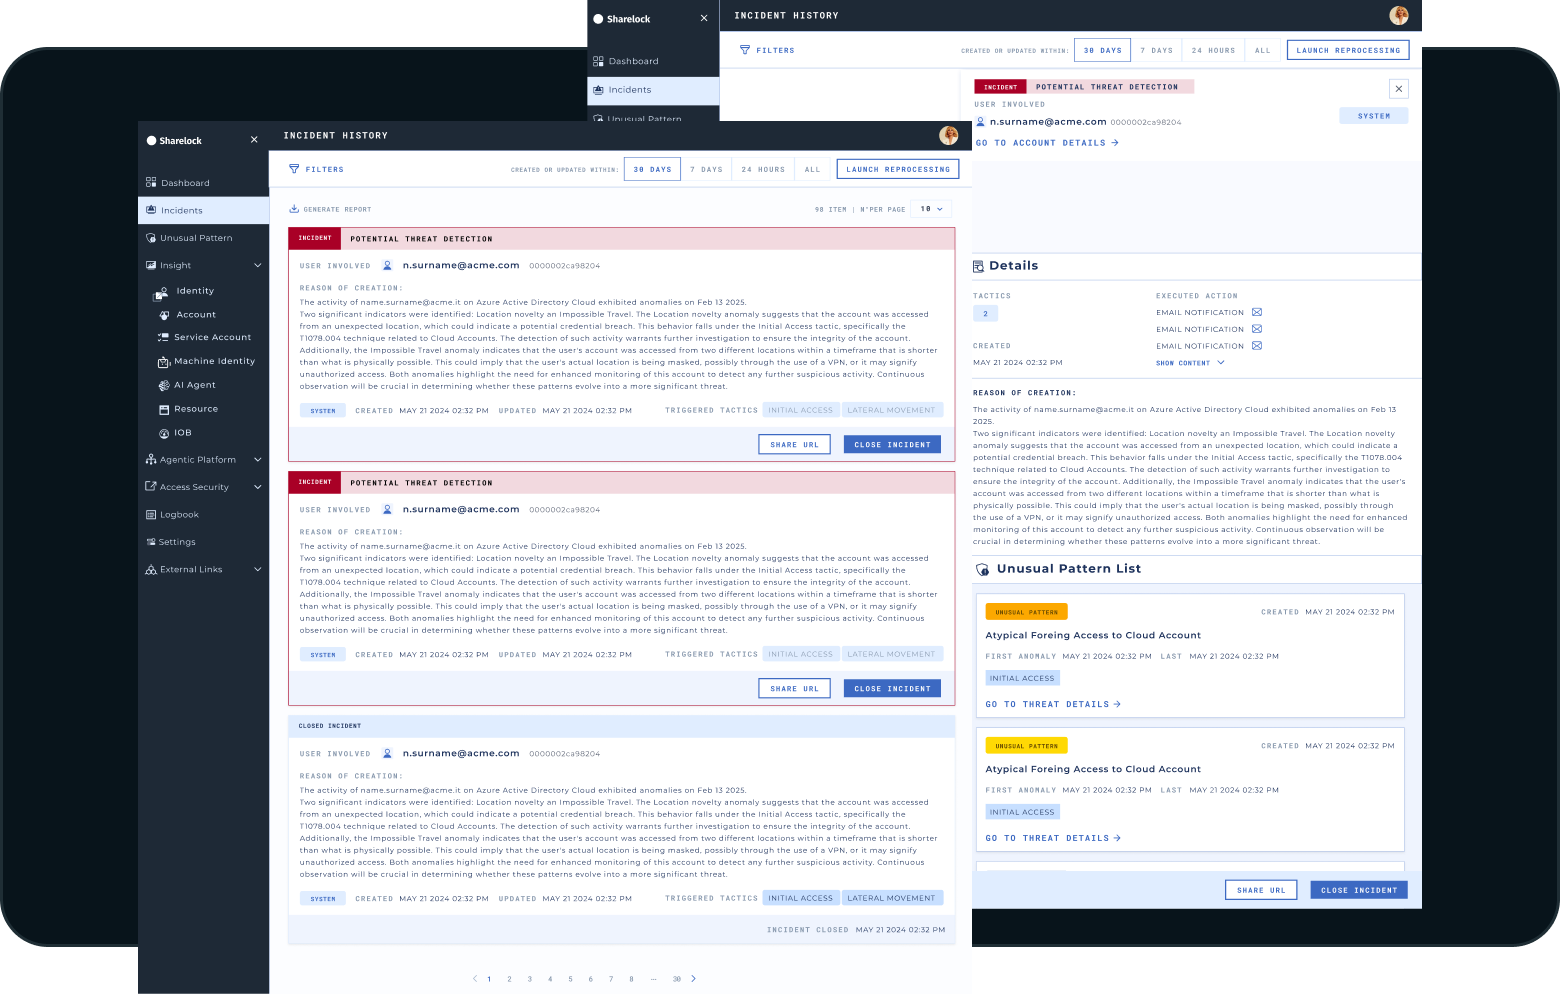
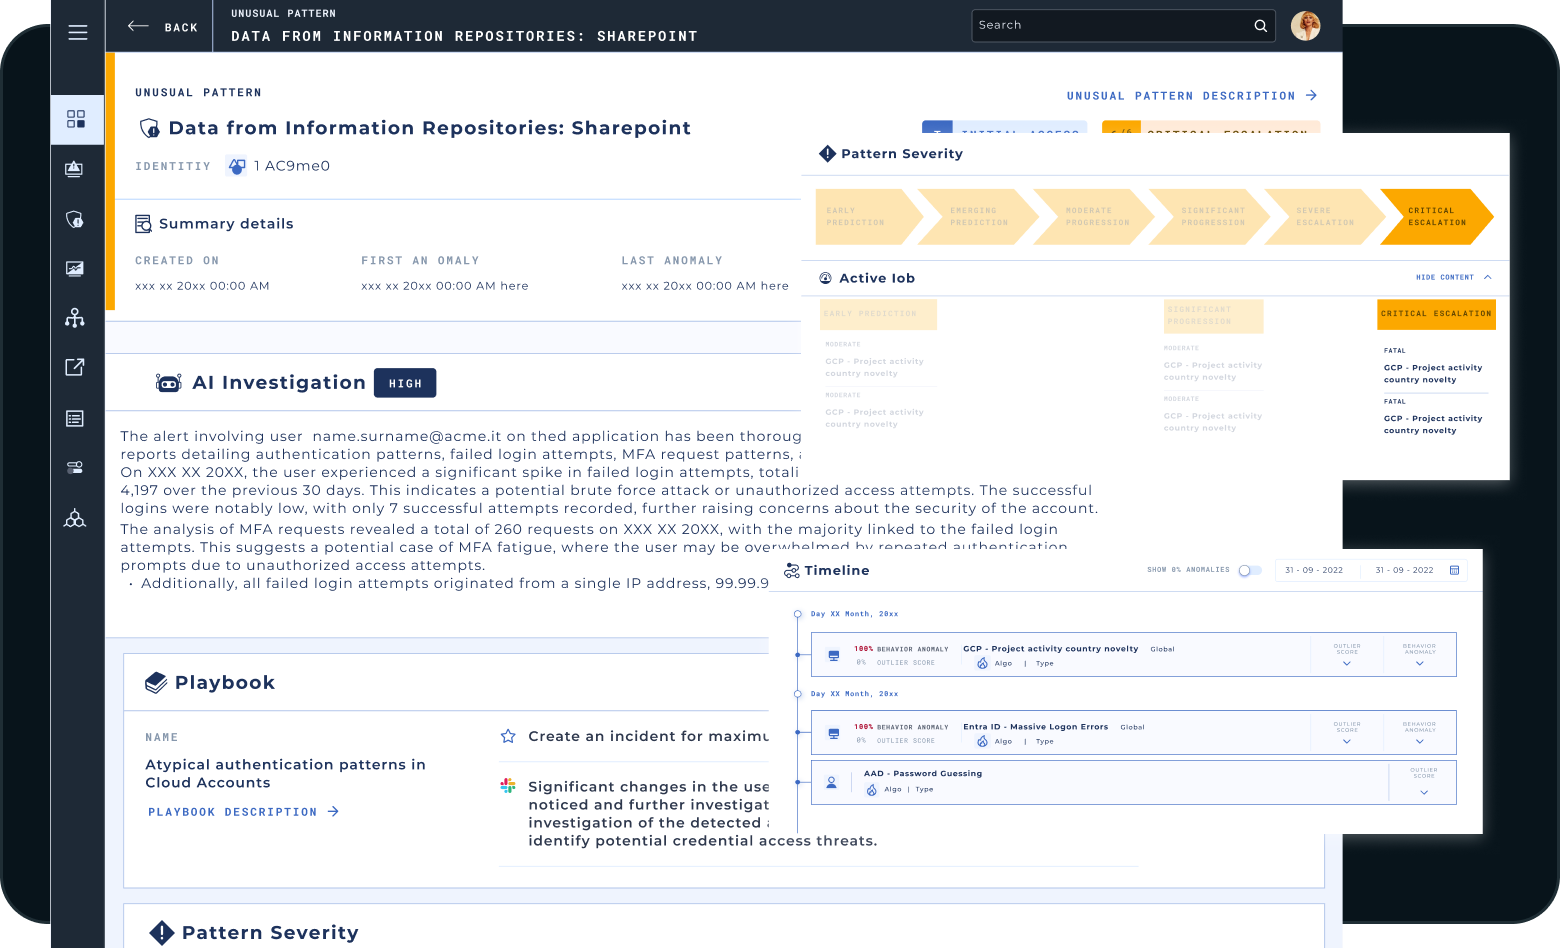
Continuous detection: no static rules, no blind spots
THE UNFAIR ADVANTAGE
Infrastructure-aware: from cloud native to legacy mainframes.
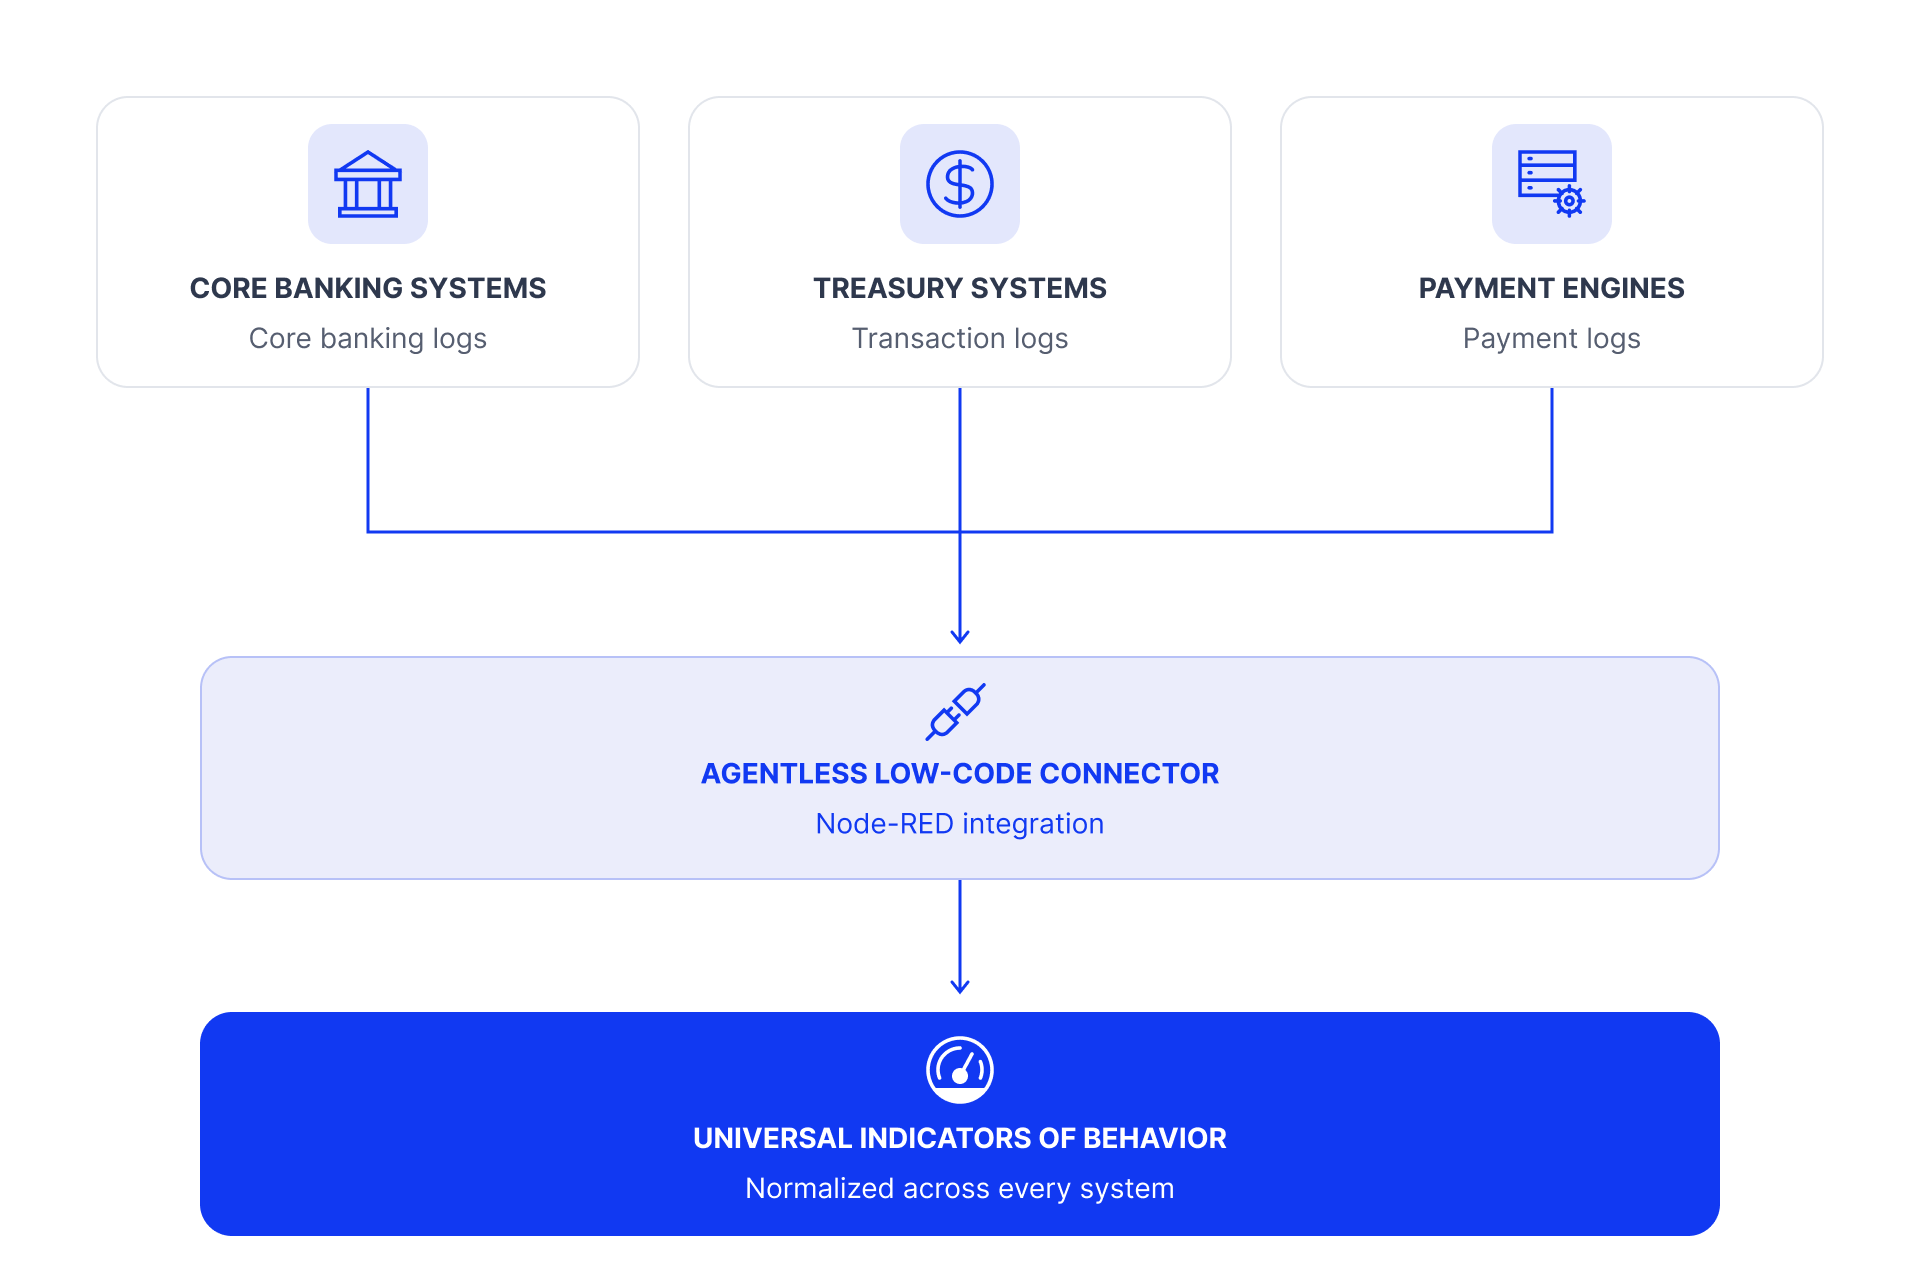
Most ITDR solutions only protect modern SaaS apps. Sharelock is built for the reality of enterprise infrastructure. Thanks to our agentless, low-code Node-RED integration, we normalize identity logs from custom banking apps, homegrown treasury systems, and legacy mainframes, applying universal Indicators of Behavior (IoB) everywhere.
USE CASES
Detecting the undetectable
THE SOLUTION: THE SHARELOCK PLATFORM
One platform, limitless security
Unify human and non-human identities across on-prem and cloud environments, replacing point solutions with a single, comprehensive identity security platform.
Prevent
Identity Security Posture Management
Discover and close identity gaps before attackers find them. Automated hygiene for misconfigured accounts, orphaned privileges, shadow admins, and non-compliant access across hybrid, cloud, and on-prem environments.
Explore PreventionDetect
Identity Threat Detection
No static rules. No alert storms. Sharelock's behavioral AI monitors every access event and entity behavior to detect credential misuse, privilege escalation, and lateral movement in real time, across every environment.
Respond
SIA - Security Investigation Autopilot
The case is closed before your analyst reads the alert. SIA autonomously correlates signals, maps the attacker's path, enforces remediation, and generates a complete audit trail without a single manual query.
AI-Driven Identity Security: Precision, Speed, Efficiency
Revolutionize identity protection with advanced AI that accelerates investigations, automates responses, and enforces security posture.

Investigate and Respond Instantly

Enforce Proactive Identity Security

Boost Efficiency with Automation

The leading Agentic AI Autopilot for autonomous identity threat detection and response (ITDR) and cloud entitlement protection.





