Identity security that prevents, detects, and responds without waiting for a human
Most identity security tools detect the threat and stop there. Sharelock's Agentic AI takes the investigation to completion, autonomously mapping the attack, enforcing remediation, and closing the case before your analyst reads the first notification.
Ask for a demo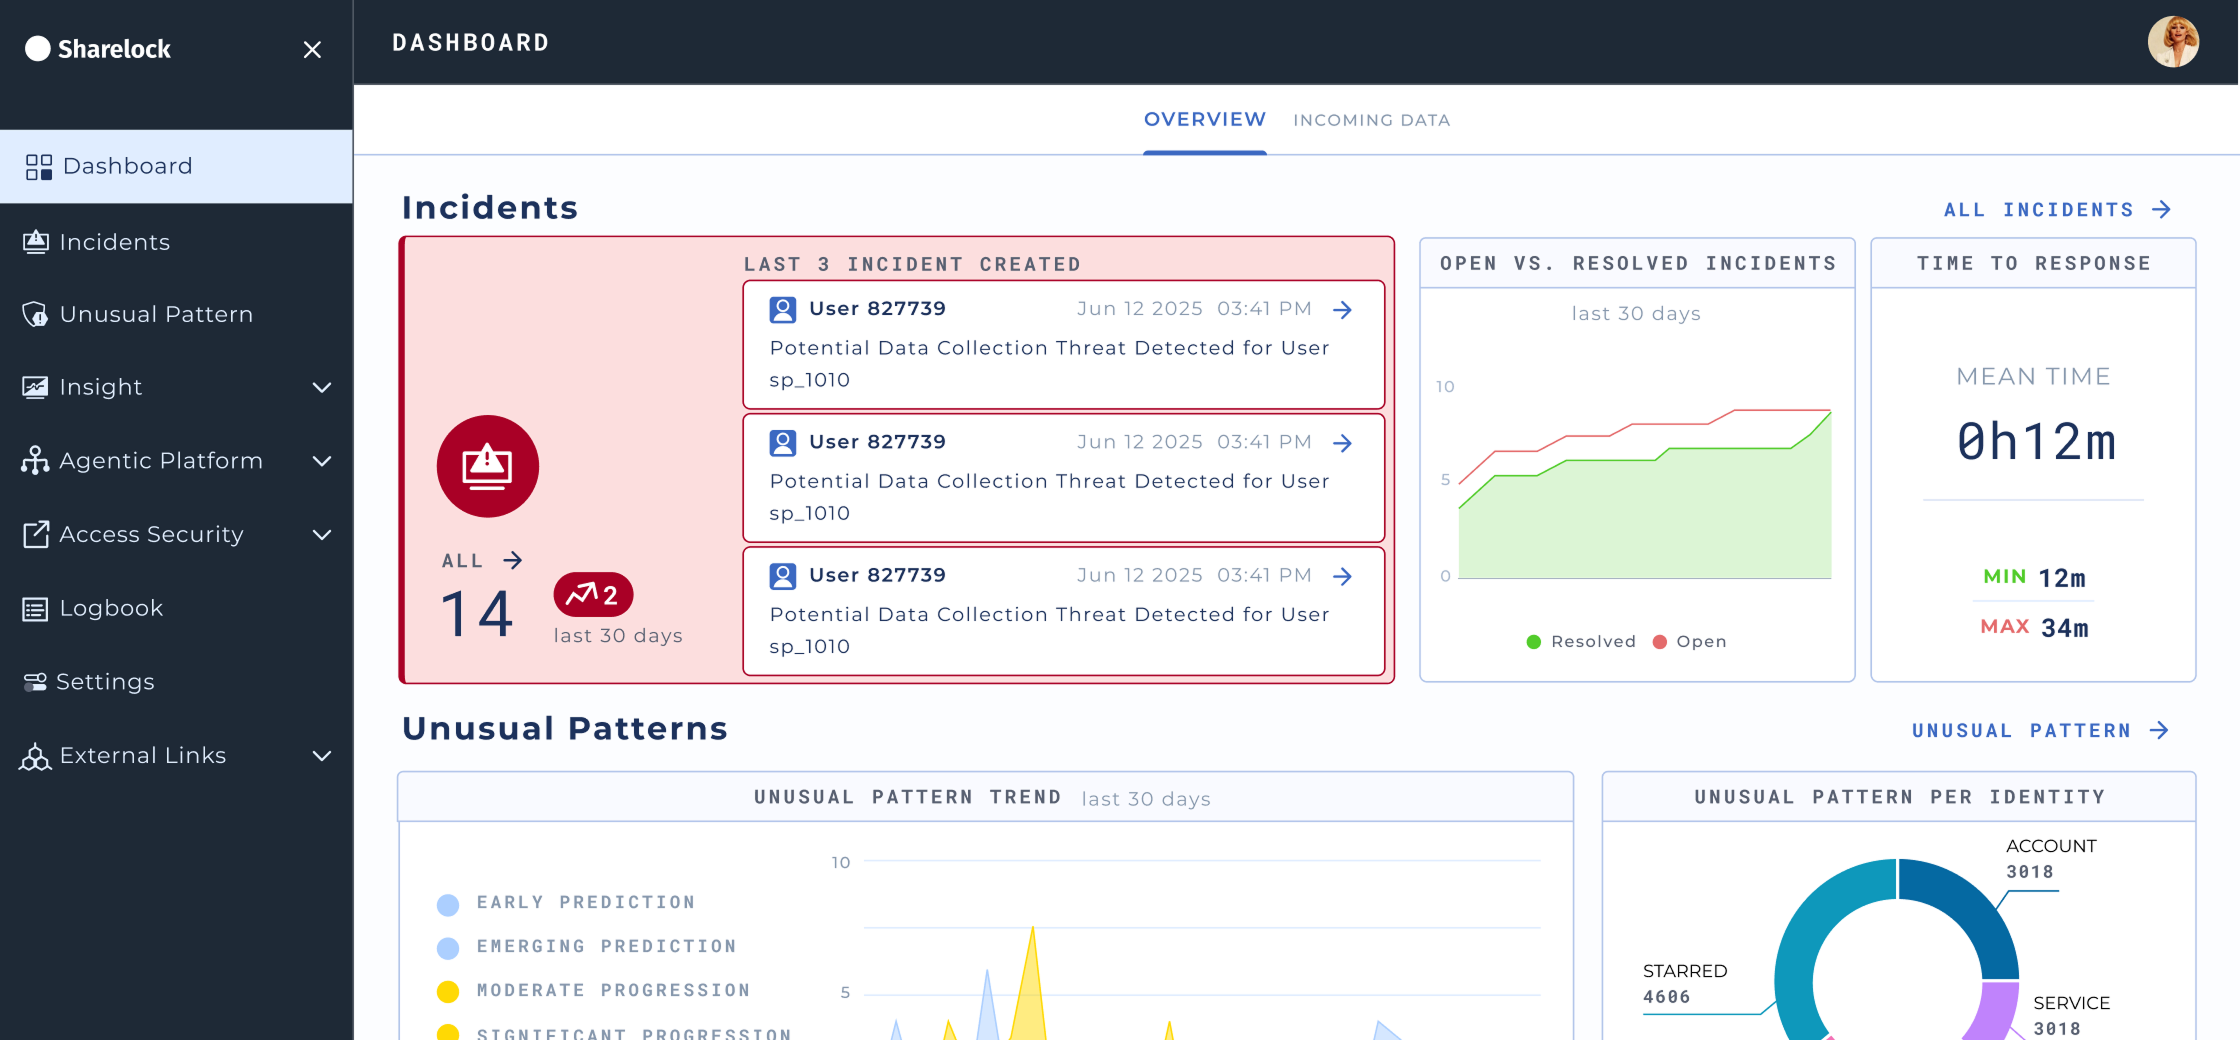
One AI engine. The entire identity attack lifecycle.
Sharelock is the only platform that connects identity posture management before an attack, behavioral threat detection during, and autonomous investigation after, with a single Agentic AI engine running continuously across all three phases.
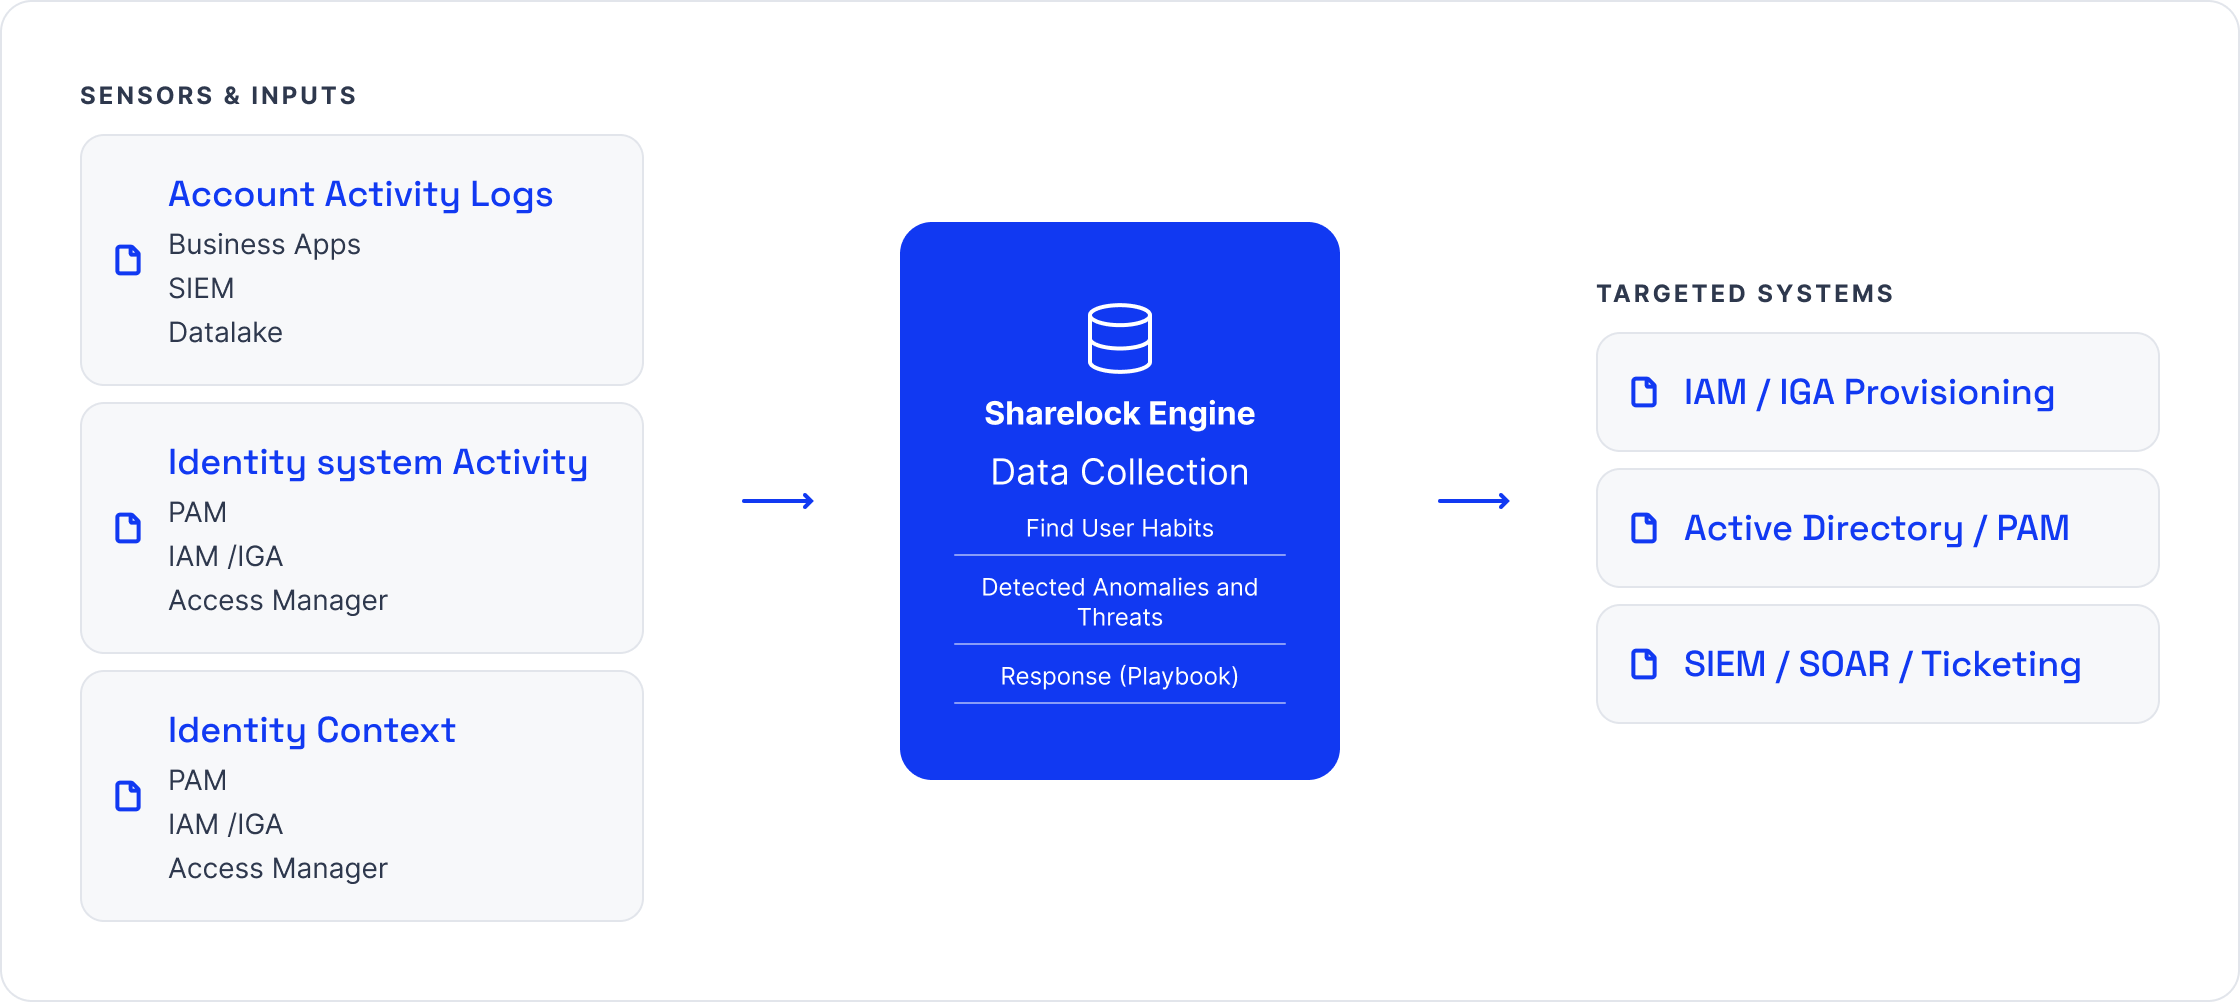

No switching tools. No manual handoffs between systems. No alert that goes uninvestigated because the queue was too long.
OUR PRODUCT
Discover Sharelock in Action
Unleash the power of AI Identity Security to revolutionize your defense strategies with state-of-the-art technology.
Ask for a demo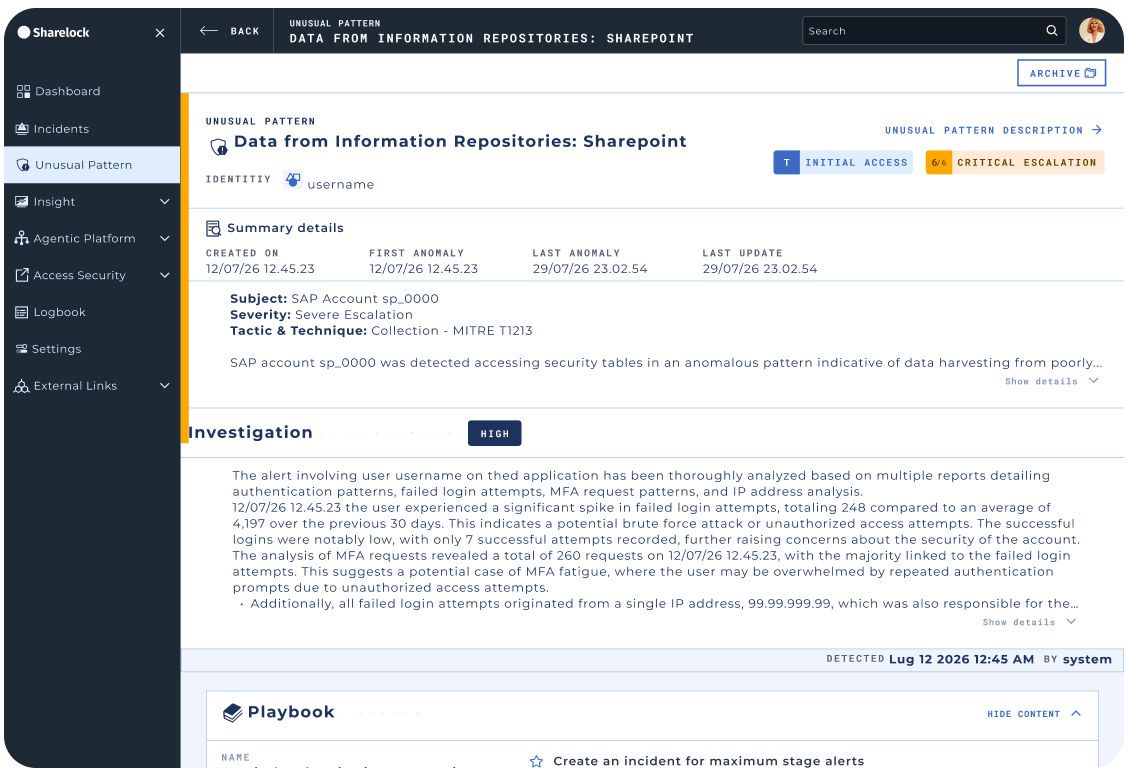
What makes Sharelock different
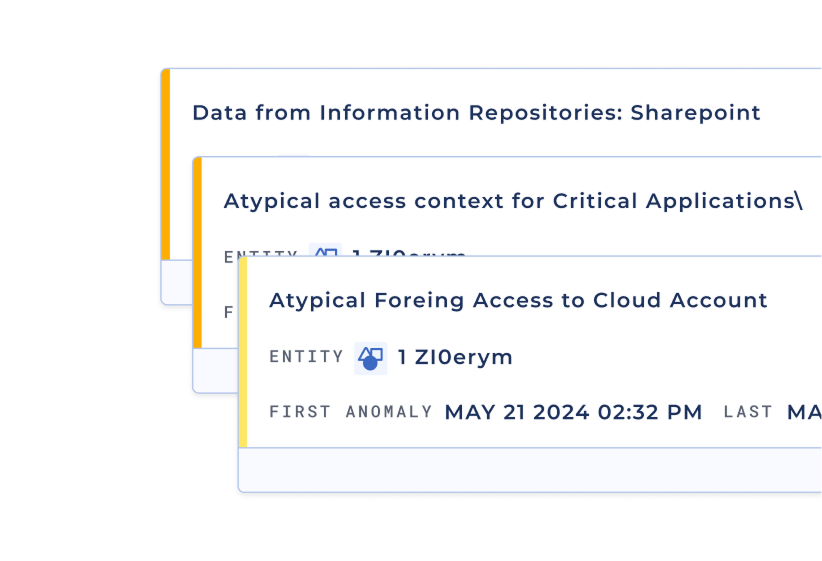
Detection without rules, or false alarms
Unsupervised machine learning learns your environment and flags anomalies, No static rules, no known-signature dependency.
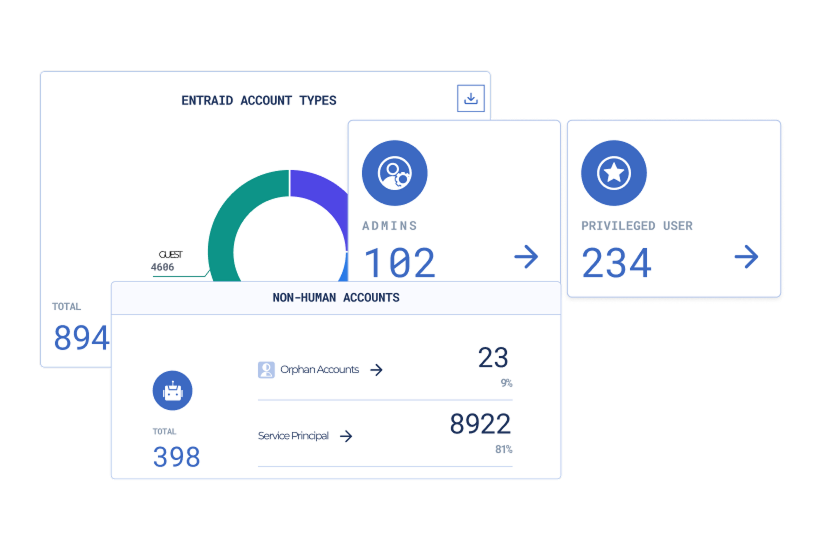
Every identity. Human, non-human, and AI agent.
Service accounts, API keys, AI agents, privileged users. Sharelock maps and monitors every identity across hybrid, cloud, and on-prem environments.
No code, No engineers, No waiting
No code needed: build unlimited agentic processes from the UI, without engineering resources or integration sprints.
THE SOLUTION: THE SHARELOCK PLATFORM
One platform, limitless security
Unify human and non-human identities across on-prem and cloud environments, replacing point solutions with a single, comprehensive identity security platform.
Prevent
Identity Security Posture Management
Discover and close identity gaps before attackers find them. Automated hygiene for misconfigured accounts, orphaned privileges, shadow admins, and non-compliant access across hybrid, cloud, and on-prem environments.
Explore PreventionDetect
Identity Threat Detection
No static rules. No alert storms. Sharelock's behavioral AI monitors every access event and entity behavior to detect credential misuse, privilege escalation, and lateral movement in real time, across every environment.
Explore DetectionRespond
SIA - Security Investigation Autopilot
The case is closed before your analyst reads the alert. SIA autonomously correlates signals, maps the attacker's path, enforces remediation, and generates a complete audit trail without a single manual query.
Explore RespondAI-Driven Identity Security: Precision, Speed, Efficiency
Revolutionize identity protection with advanced AI that accelerates investigations, automates responses, and enforces security posture.

Investigate and Respond Instantly

Enforce Proactive Identity Security

Boost Efficiency with Automation
Why security teams choose Sharelock over point solutions

No rules. No policies. No known-threat dependency.
No predefined rules, no known attack signatures. Unsupervised ML learns your baseline and surfaces anomalies, including attacks never seen before.

Prevent attacks that haven't happened yet
ISPM continuously discovers identity gaps, misconfigured accounts, excessive privileges, stale access, shadow admins before any attacker can exploit them.

Your existing identity stack stays. Sharelock makes it better.

The analyst reads the notification. The case is already closed.
SIA runs the full investigation lifecycle autonomously: alert triage, lateral movement mapping, remediation enforcement. Analysts review outcomes, not queues.

Service accounts, API keys, AI agents, all protected.
Non-human identities are the fastest-growing, least-monitored attack surface. Sharelock applies the same behavioral intelligence to them as to human users.

Zero code, unlimited agentic processes
Build unlimited agentic processes from the UI. Zero code, zero engineering, full flexibility to adapt as your security needs evolve.
Sharelock investigates identity alerts in 31 seconds. Autonomously
See the Autopilot in action, no slides, no pitch.